Actions
Support #5370
closed
KS
OD
The problem of Suricata reading Wireshark's pcap package
Support #5370:
The problem of Suricata reading Wireshark's pcap package
Description
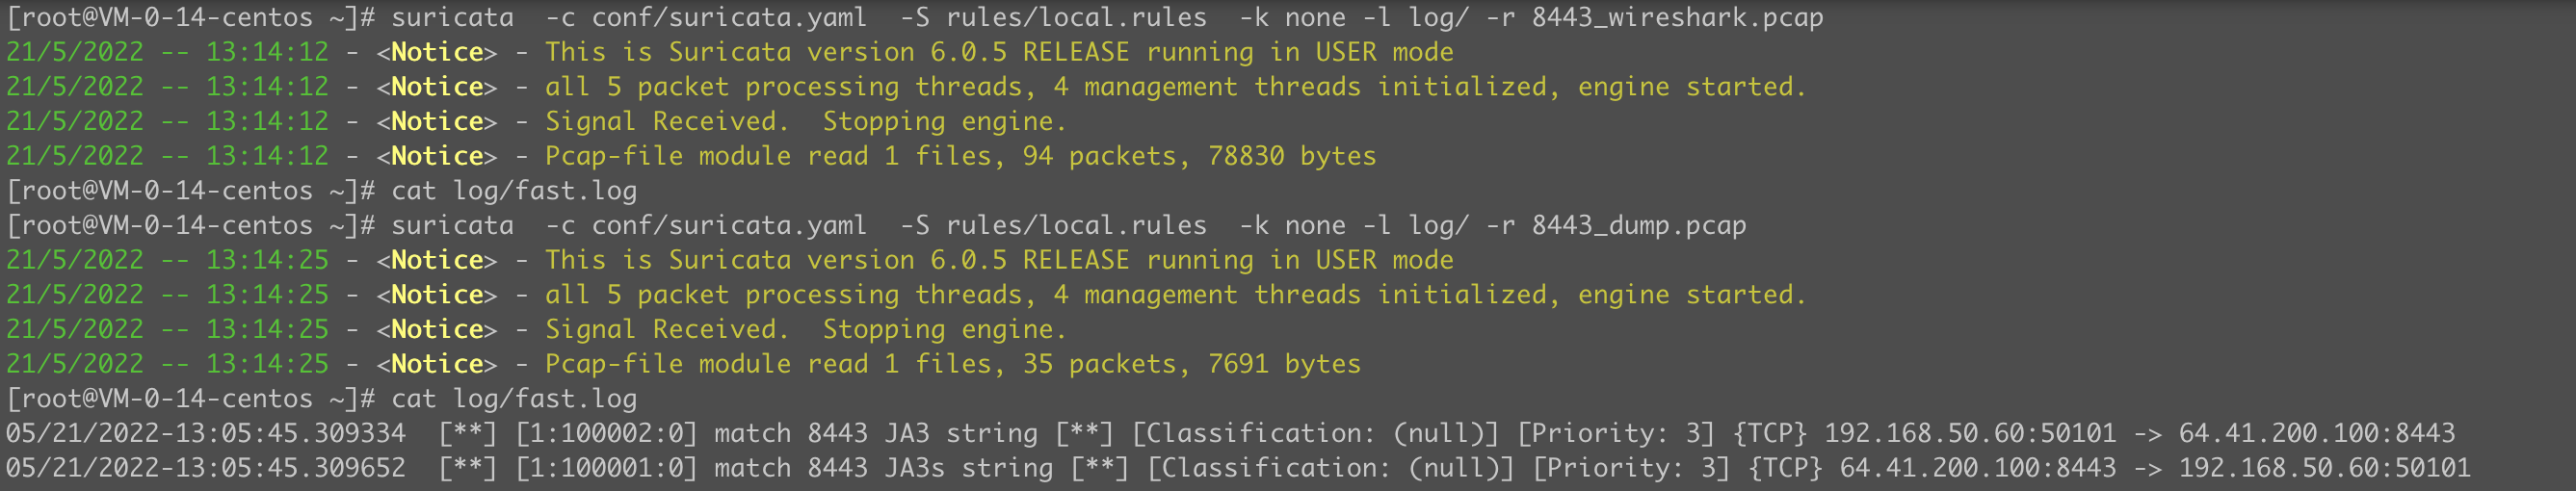
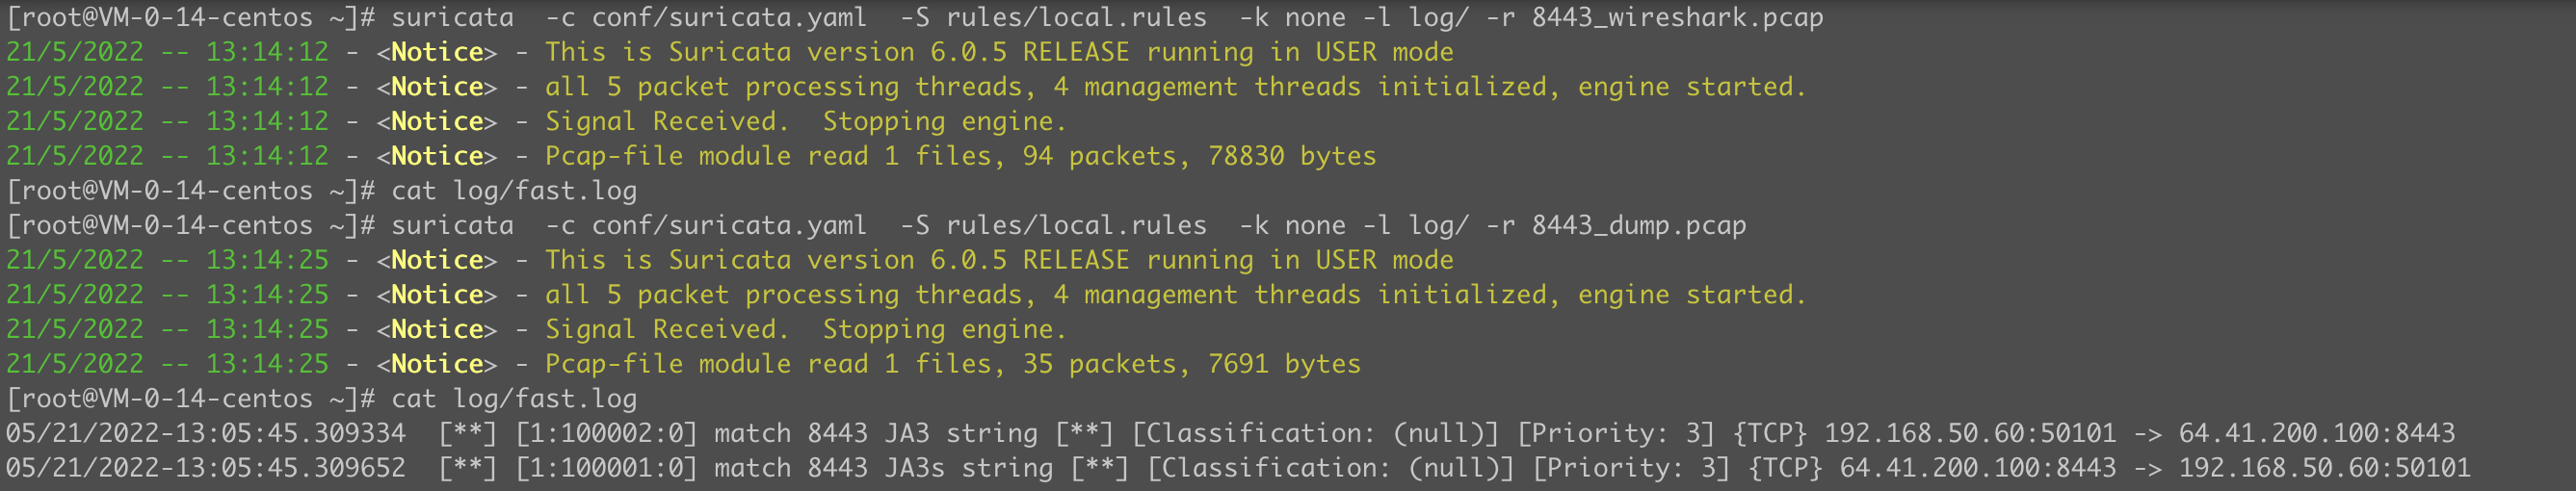
Hello, I'm learning IDs. I wrote a Suricata rule. I used Wireshark and tcpdump to export two pcap packages and read them with the - R parameter. The result is that only the pcap package of tcpdump can be matched.
Files
Actions